Security Compliance
Data security and compliance are not afterthoughts at Northlight — they are built into the way we work from day one. When you share financial data with an outsourced accounting partner, you are placing a significant degree of trust in their systems, their people, and their processes. We take that seriously. From secure file sharing and encrypted data handling to confidentiality agreements and access control policies, we have put thoughtful measures in place across every stage of our operation to handle your financial information with care, discretion, and professionalism. Here is how we approach data security across everything we do.
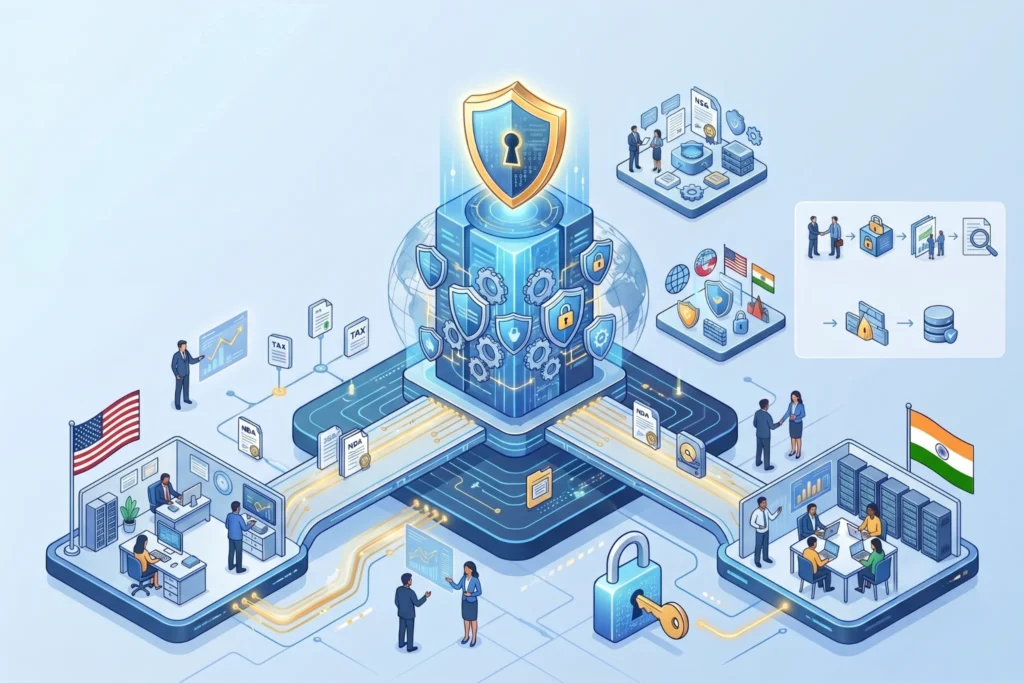
How Northlight Approaches Data Security Across Every Client Engagement
Handling sensitive financial data responsibly is one of the most important aspects of any outsourced accounting relationship. We recognise that the businesses and individuals who work with us are sharing information that is private, commercially sensitive, and in many cases legally protected — and we treat it accordingly.
We have put deliberate measures in place across our systems, processes, and people to reduce the risk of unauthorised access, data loss, and confidentiality breaches. These measures are reviewed and updated regularly as technology, regulation, and best practice evolve. While no system can offer absolute guarantees, we work continuously to ensure that the way we handle your data reflects a genuine and ongoing commitment to doing it responsibly.
Below is a transparent overview of the specific measures we have in place across our operation.
Confidentiality Documented Before Anything Else
Before any client data is accessed or processed, we put formal confidentiality documentation in place. Every engagement begins with a signed confidentiality agreement covering how your information will be handled and who within our team will have access to it.
Every member of our team also signs a personal non-disclosure agreement as a condition of working with us — creating accountability at both the organisational and individual level.
Confidentiality Built Into How We Work — Not Just What We Sign
Confidentiality at Northlight is not just a document — it is a principle embedded in how our teams are trained and how data access is structured across our operation.
Client data is treated as strictly need-to-know within our organisation. Access is limited to individuals directly involved in your engagement, and our team receives regular guidance on their data handling responsibilities throughout their time with us.
Secure Channels for Every Document Transfer
We do not rely on standard email attachments for transferring sensitive financial data. We use encrypted file sharing platforms that require authentication before access, create an auditable access record, and encrypt files both in transit and at rest.
We ask all clients to use these designated channels for sharing sensitive documents — and we are happy to walk you through the process if you are unfamiliar with the tools we use.
Controlled Access — Only Who Needs It
Access to your data within our operation is granted on a strict need-to-know basis. Only individuals directly assigned to your engagement can see your information — with access levels defined by role, reviewed regularly, and removed immediately when team members change roles or leave.
We enforce these boundaries through platform-level permission controls across our accounting software and file sharing systems — supported by multi-factor authentication where platforms allow it.
Reducing the Risk of Data Loss
The cloud platforms we work within maintain their own backup and recovery infrastructure as a baseline. Where we hold or process client data in our own systems, we maintain regular backup schedules and periodically verify that data is recoverable.
We want to be transparent — our backup procedures are designed to reduce the risk of data loss, not eliminate it entirely. No backup system is infallible and we think it is more honest to say so clearly.
Encryption Applied Across Our Systems
The platforms we use for accounting, file sharing, and communication employ recognised encryption standards — covering data in transit and data at rest. Encryption is a baseline requirement in every platform we select, not an optional feature.
We apply security updates promptly when they become available and conduct regular reviews of the tools we use to ensure they continue to meet the standards we hold ourselves to.
The Infrastructure We Use to Handle Your Financial Data Responsibly
The security of your financial data depends not just on policies and agreements but on the technical environment in which that data is stored, processed, and transmitted. We have made deliberate choices about the infrastructure we use — selecting platforms and systems that meet recognised security standards and that give us meaningful control over how client data is handled.
Cloud Platforms With Built-In Security Standards
We work primarily within established, widely-used cloud accounting and document management platforms — Xero, QuickBooks, Sage, FreeAgent, and others — that maintain their own robust security infrastructure, including data centre redundancy, encryption, and access controls. We do not build our own infrastructure from scratch — we work within platforms that have invested significantly in security as a core part of their product.
Multi-Factor Authentication Where Supported
Where the platforms we use support multi-factor authentication, we implement it across our team accounts as standard — adding an additional verification step that reduces the risk of unauthorised access even in the event that login credentials are compromised.
Regular Software and Security Updates
Outdated software is one of the most common vectors for security vulnerabilities. We maintain a practice of applying available security updates and patches promptly across the systems and tools our team uses — reducing our exposure to known vulnerabilities in a timely manner.
Controlled Use of Third-Party Tools
We review any third-party tool or platform before it is adopted into our workflow — considering its data handling policies, its security credentials, and whether it meets the standards we apply across the rest of our operation. We do not use tools that handle client data without first satisfying ourselves that they meet a reasonable standard of security.
Staff Awareness and Training
Technical controls are only as effective as the people operating within them. Our team receives regular guidance on data security awareness — covering how to identify phishing attempts, how to handle sensitive data appropriately, and how to escalate any situation that could represent a security risk. Human error remains one of the most significant causes of data incidents across all industries, and we take a practical approach to reducing it through ongoing awareness rather than assuming that policies alone are sufficient.
Incident Response Awareness
We have a defined process for identifying, escalating, and responding to potential data security incidents — including notifying affected clients and relevant regulatory bodies where required by applicable data protection law. We hope never to need it, but we believe it is responsible to have a clear process in place rather than to respond to an incident without one.
We Follow Global Security Standards
What You Should Know About How We Handle Your Data
We treat your data as sensitive by default — every piece of client information is handled with care regardless of how routine it might appear.